AI Governance
End-to-end review of model usage, data flows, vendor terms, disclosures, and automated decision risk across your product surface.
- Model & data flow mapping
- Training-data and vendor terms
- Disclosure gap analysis
ComplyMynt helps AI and SaaS companies identify, prioritize, remediate, verify, and continuously monitor compliance, AI governance, privacy, consent, accessibility, and cybersecurity risk — before customers, procurement teams, or regulators find it.
Risk domains reviewed
Assessment checks
Stages: scan to monitor
Typical report window

Reviewed against
Inside the audit
Our engine crawls your live surfaces, replays consent and checkout flows, inspects network traffic and model responses, then routes every signal to the specialist who owns that risk domain.
Scorecards
Domain-level scores, weighted by severity and exposure, tracked across re-verification cycles. The figures below are an illustrative sample, not client data.
Privacy
Illustrative sample
Consent
Illustrative sample
Accessibility
Illustrative sample
Security surface
Illustrative sample
Services
Run them together for full coverage, or start with the surface causing the most pressure right now.
End-to-end review of model usage, data flows, vendor terms, disclosures, and automated decision risk across your product surface.
Tag, tracker, and consent-banner analysis mapped to GDPR, CPRA, and state privacy expectations — with evidence you can hand to counsel.
Forms, SMS flows, call scripts, and lead-gen paths reviewed for express written consent, revocation, and record-keeping defects.
We replay your banner against real tag firing order, revocation, and record retention so your consent stack matches your policy claims.
WCAG 2.2 AA testing combining automated scans with manual keyboard, screen-reader, and contrast validation on real user journeys.
Externally observable security posture: headers, exposure, authentication surfaces, and disclosure readiness — no intrusive testing.
A full-site review of legal, privacy, accessibility, and technical signals that enterprise buyers and regulators evaluate first.
Board-ready, multi-domain assessments with procurement-friendly deliverables, vendor questionnaires, and quarterly re-verification.
Industries
Risk looks different in a model-serving platform than in a DTC storefront. Our review adapts.
Model disclosures, training data provenance, output risk, and AI Act readiness.
DPAs, subprocessors, enterprise security questionnaires, and consent at scale.
PHI handling boundaries, vendor sharing, tracking pixels, and accessibility mandates.
Consent, disclosures, and marketing compliance under regulatory scrutiny.
Cookies, retargeting, SMS marketing consent, and checkout accessibility.
Lead-handoff consent, client pixel governance, and TCPA-safe capture.
Confidentiality, records management, and accessible client portals.
Multi-business-unit assessments, procurement reviews, and board reporting.
The audit desk
Privacy counsel, accessibility engineers, and security reviewers sign off on every finding before it reaches your board.
Why ComplyMynt
We review model usage, automated decisions, and data provenance — not just cookie banners from 2019.
Every finding carries evidence, reproduction steps, an owner, and an estimated fix cost.
Fixed scope and fixed timelines. Most reports land inside two weeks of kickoff.
Least-privilege access, encrypted evidence storage, named handlers, destruction on request.
Board-ready summaries that survive procurement, security questionnaires, and diligence.
Remediation engineers hand you pull requests, not a list of recommendations.
How it works
A 30-minute call plus a short questionnaire. We define surfaces, jurisdictions, and success criteria in writing.
Read-only crawling, consent capture, network trace review, and documentation intake under NDA.
Findings are scored by likelihood, exposure, and remediation cost — no generic severity labels.
A board-ready report plus an engineer-ready backlog, delivered in a live walkthrough with your team.
Our engineers implement fixes alongside your team, or hand off precise specifications and tests.
Scheduled re-verification keeps closed findings closed and catches new regressions.
Sample findings
Redacted excerpts from real reports. Every entry ships with evidence and reproduction steps.
Six third-party trackers set identifiers on first paint, ahead of any banner interaction, in all tested EU sessions.
Model-assisted scoring affects user outcomes with no disclosure, opt-out path, or human review documented.
Checkout capture bundles marketing SMS into terms acceptance and stores no timestamped consent record.
Custom dropdowns trap focus at step two, blocking screen reader and keyboard-only account creation.
Findings workspace
Track severity, ownership, evidence, and closure in one shared surface — with drift alerts when a fix regresses.
Explore the sample workspace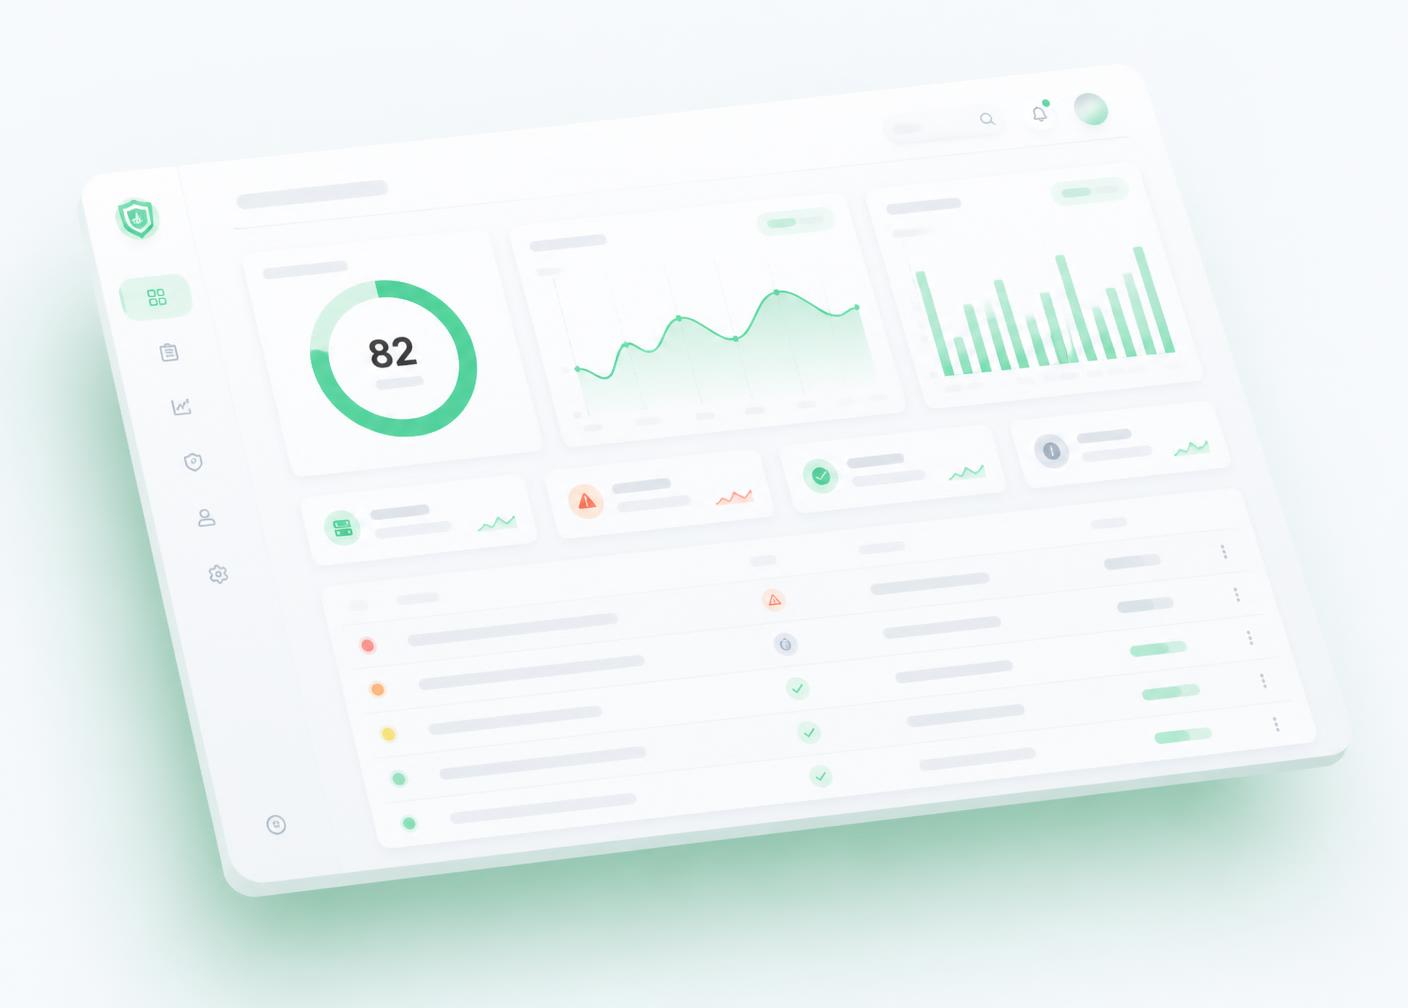
Pricing
Four audit packages, plus continuous monitoring. Every price is quoted and locked before work begins.
The core compliance surface, fully evidenced.
$2,995
one-time · single website or product
Deeper evidence across your full public surface.
$6,995
one-time · up to 3 websites or products
Manual depth and board-ready documentation.
$12,995
one-time · unlimited products in scope
Continuous assurance for regulated scale.
Starting at $35,000
annual program
We don't sell a fixed remediation package. Once your findings register is delivered, we scope engineering work against the real defects and send a fixed, line-item quote.
Ongoing
An audit is a snapshot. Monitoring keeps closed findings closed and catches drift the week it happens.
Always-on scanning for a single product.
$499
per month
Weekly coverage across multiple products.
$1,250
per month
Custom Enterprise Programs Available
Starting at $3,500
per month
Continuous Monitoring is recommended after completing a ComplyMynt audit to establish a compliance baseline.
The journey
One accountable path from discovery to continuous coverage. Every stage has a defined input, output, and owner.
Automated crawl of your public and authorized surfaces, consent flows, tags, and model responses.
Specialists verify every signal by hand and score it by likelihood, exposure, and remediation cost.
Remediation engineers deliver pull requests and specifications, or hand your team precise tickets.
Each fix is re-tested against the original evidence before a finding is marked closed.
Scheduled re-verification catches regressions and new exposure as your product ships.
FAQ
Resources
Practical writing for teams shipping AI features under real regulatory pressure.
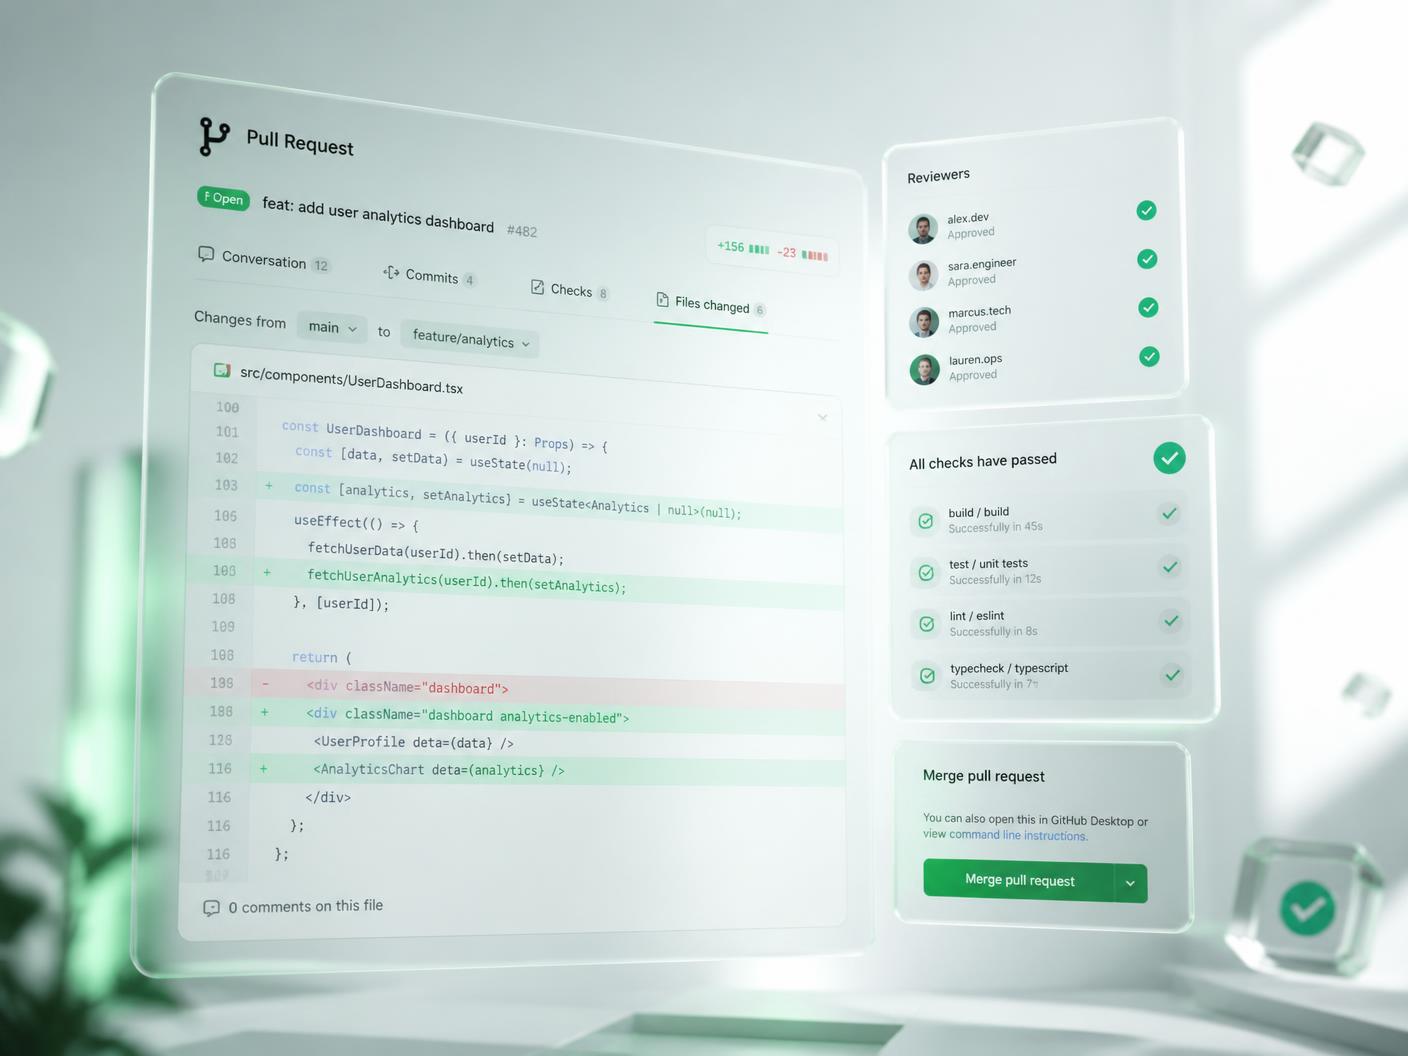
Remediation
Our engineers open pull requests against your repo, rebuild consent capture, patch accessibility defects, and re-verify each fix before it is marked closed.
Pull requests
How fixes land
Acceptance criteria
Every ticket includes
Re-verified
Before close
Tell us your surfaces and timeline. We reply with scope, a fixed price, and a delivery date within one business day.